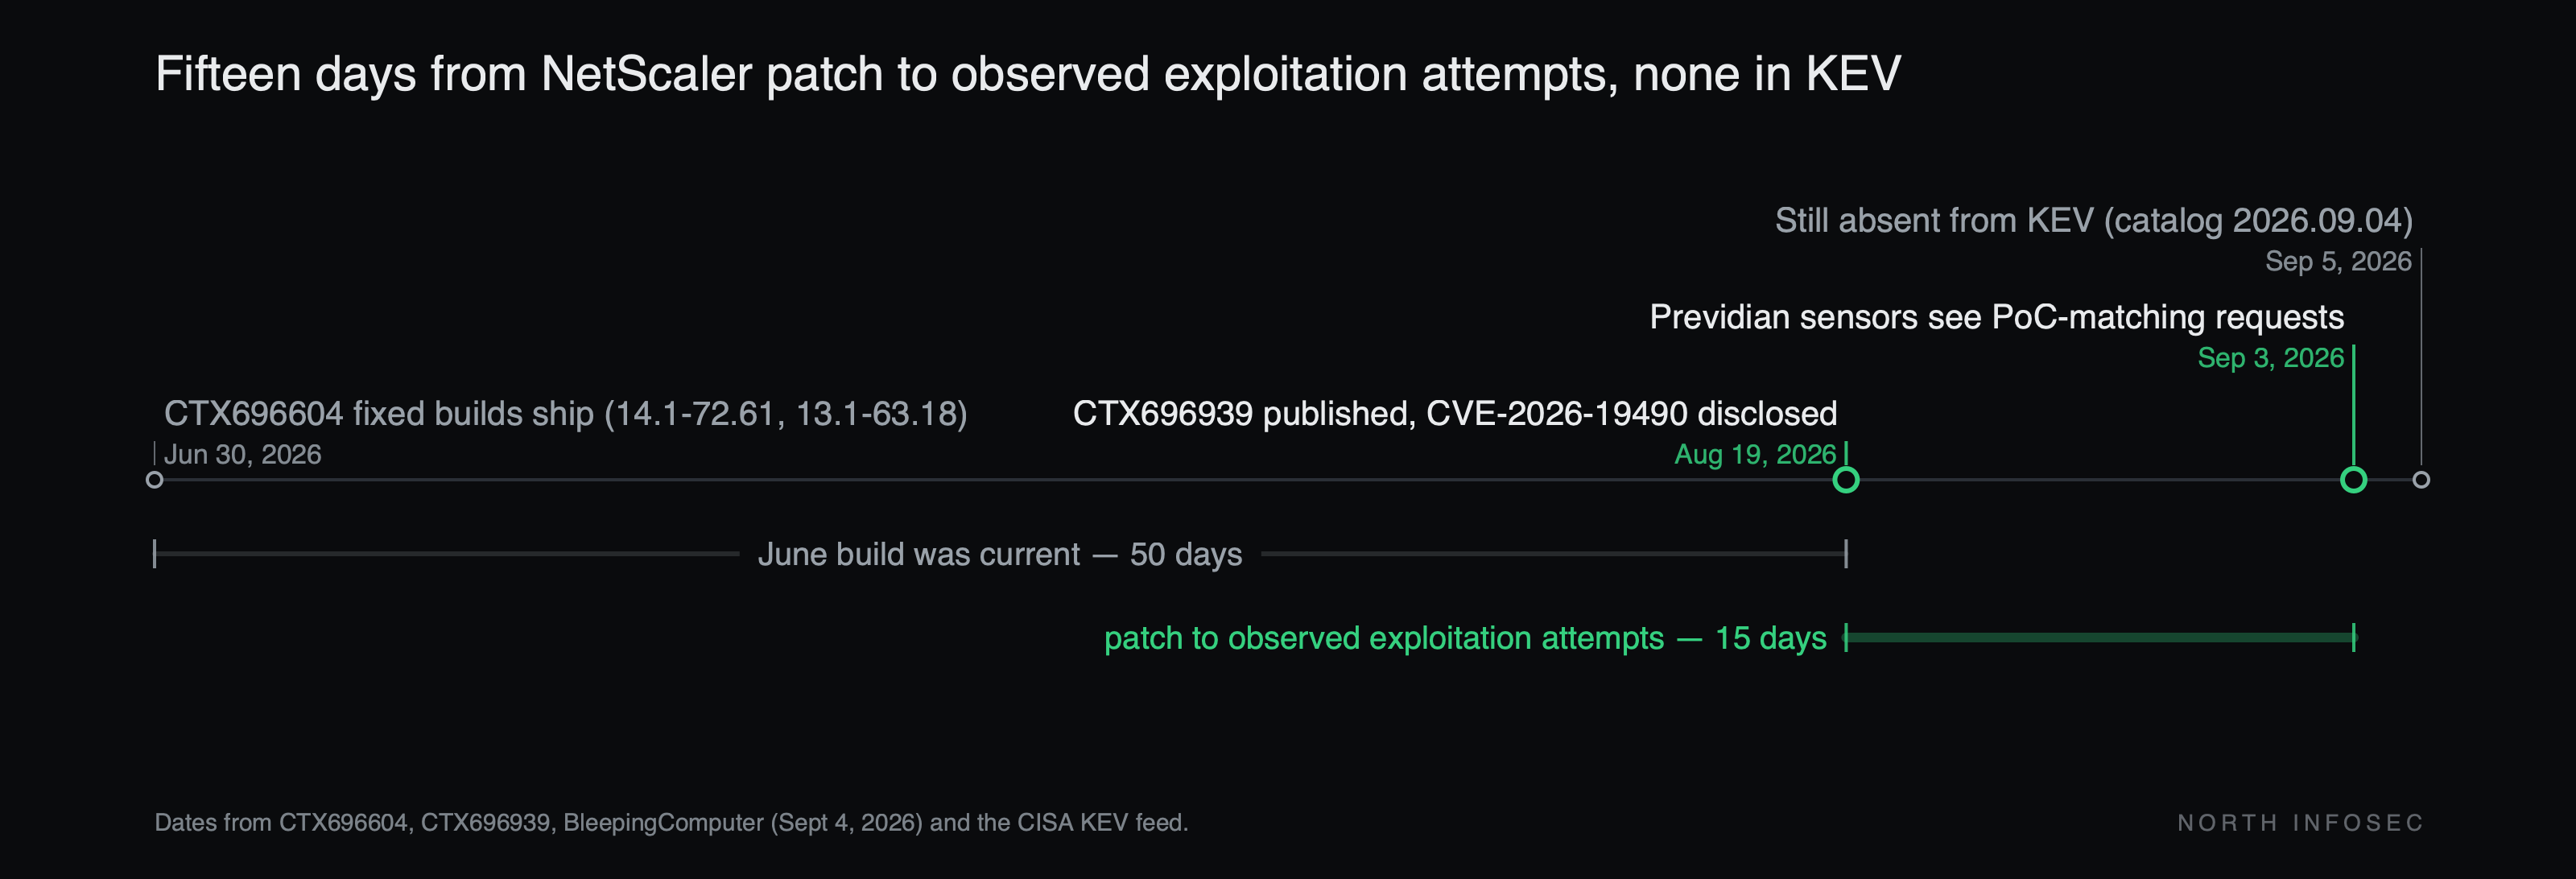
Cloud Software Group published CTX696939 on August 19, 2026, fixing CVE-2026-19490, an authentication bypass in NetScaler ADC and NetScaler Gateway scored CVSS 4.0 9.3. On September 3, one of Previdian's NetScaler sensors "received requests matching the PoC from three distinct source IPs, geolocated to Australia, the United States and Germany," founder Ryan Dewhurst told BleepingComputer the next day. Citrix has added no exploitation statement to the bulletin, and CISA's Known Exploited Vulnerabilities catalog, version 2026.09.04, does not list the CVE as of September 5. Fifteen days from patch to observed attempts, and KEV membership was never going to be the trigger.
Coverage compresses the precondition to one sentence: Gateway or AAA, plus a SAML action on newer builds. That is accurate and the wrong shape for triage: the bulletin's precondition is a table with a build number in every row. The previous piece in this series argued for reading the clause per CVE. For this CVE the clause changes per build.
What the bulletin says
The CVE row reads "Authentication bypass using an alternate path," CWE-288, credited to Samarth Vashisht from the pen-test team at JPMorgan Chase. The precondition column, quoted as published:
- "14.1-43.56 or later: Applicable only when configured with a SAML action AND NetScaler is configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver"
- "14.1-66.68-FIPS or later: Applicable only when configured with a SAML action AND NetScaler is configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver"
- "14.1-43.55 or earlier: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver"
- "13.1-61.28 or later: Applicable only when configured with a SAML action."
- "13.1-61.27 or earlier: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver"
- "13.1 FIPS: Applicable when configured with Gateway (SSL VPN, ICA Proxy, CVPN, RDP Proxy) or AAA vserver."
Fixed builds are 14.1-73.32, 13.1-63.21, 14.1-73.32 FIPS, and 13.1-37.277 for 13.1 FIPS and 13.1 NDcPP.
Three populations under one headline
Read as a table, that is three groups of operators, and "requires SAML" is true for one of them.
The gated group runs 14.1-43.56, 14.1-66.68-FIPS or 13.1-61.28 or later. That includes everyone who applied June's CTX696604, whose fixed builds were 14.1-72.61 and 13.1-63.18. For this group the headline holds: with no SAML action in running config, the bulletin says the CVE does not apply.
The ungated group runs 14.1-43.55 or 13.1-61.27 or earlier. Any Gateway or AAA vserver is sufficient. Those builds also predate the June advisory, so CVE-2026-8451 and CVE-2026-8452 are open on the same appliance too.
The third group is 13.1 FIPS. That row has no build split: Gateway or AAA is enough at every build. The fix is 13.1-37.277, and the June FIPS and NDcPP fix, 13.1-37.272, sits below it. The 14.1 FIPS line is gated from 14.1-66.68-FIPS onward, so "FIPS has no gate" is a statement about 13.1 only.
Citrix has not said why the gate exists on newer builds or what changed at 14.1-43.56.
What the bypass reaches
CWE-288 means the appliance answered a request it should have refused at the authentication front door, so the exposure to measure is what sits behind that vserver: ICA sessions, the RDP proxy, the internal web applications published through clientless VPN. Field Effect's September 4 note makes the same point: "validating deployment architecture and configuration is as important as confirming software versions."
The practice: find your row, then read the config
Two commands on every appliance. The grep strings are the bulletin's own.
show version
show running config | grep -E "add authentication samlAction|add authentication vserver|add vpn vserver"
On an ungated row, meaning 14.1-43.55 or earlier, 13.1-61.27 or earlier, or 13.1 FIPS, any vserver match means exposed and the samlAction result is irrelevant. On a gated row, exposed requires both a samlAction match and a vserver match.
The cost is unchanged from the last two advisories: someone with shell access, usually networking, runs this and relays the answer to whoever holds the ticket, usually security. The new cost is that the saved one-liner from June is wrong for part of the fleet, because the check now has a version branch. Every path ends at the same upgrade. The triage decides who goes first.
If the window is not this week, the bulletin offers no workaround. On a gated build, a SAML action that nothing binds is worth removing, since the bulletin's wording takes the appliance out of scope without it. Check the binding with show authentication samlAction first. On an ungated build or 13.1 FIPS there is no configuration answer short of removing the Gateway or AAA vserver, which is the outage the deferred upgrade was avoiding.
What to check this week
- The
show versionoutput for every NetScaler, with its precondition row written next to it. - On gated rows: does
add authentication samlActionappear, and is it bound to anything? - On ungated rows and 13.1 FIPS: any
add vpn vserveroradd authentication vserverline means exposed. - If the appliance was internet-facing on an affected build after September 3: review AAA and VPN logs for sessions with no matching authentication event.
- Does your patch tracker still record 14.1-72.61 or 13.1-63.18 as current?
As of September 5, 2026, Citrix has not confirmed exploitation, Previdian describes attempts rather than compromise, and CVE-2026-19490 is absent from KEV.
North InfoSec runs AI-assisted penetration testing and security assessments, including the edge-appliance configuration review described above. northinfosec.com