On October 28, 2026, the Akira ransomware group added a listing titled "Roberts Consulting Services" to its leak site. The aggregated record carries group_name: akira and published: 2026-10-28. The listing says the group "will upload 28gb of corporate data soon," naming "detailed employee information (passport scans, DLs, SSN), contracts and agreements, client information, financials, NDA." Those are Akira's claims, on Akira's own infrastructure. As of October 30 there is no coverage of it anywhere, no statement from the firm, and no established access vector.
What the listing proves and what it does not
The description in the listing is the victim's own marketing copy. Akira's text opens: "RCS is a full-service engineering firm specializing in Construction Materials Testing, Construction Engineering and Inspection (CEI), and QA/QC services, founded in 2013. With over 60 years of combined FDOT experience…" The firm's homepage, in the Wayback capture of May 12, 2026, carries that sentence with one hyphen's difference — "full service" — then the same founding year and the same "over 60 years of combined FDOT experience."
That overlap identifies which company is named, and nothing else. An operator who pastes a homepage has demonstrated it can read a homepage. It is not evidence about the 28 GB, the passport scans, or the SSNs.
A different field in the same record points at the wrong company. Its website value is jsrconsulting.com, which serves a solo executive-coaching practice trading as Roberts Consulting Services, LLC — a domain created May 3, 2000, thirteen years before the engineering firm in the description existed. The engineering firm's domain, rcseng.net, was created January 20, 2013. The country field is empty. Two fields in one record name two unrelated businesses, and keying off the domain names a company that was never listed. Since the listing is frequently the only disclosure there is, read it field by field.
The structure that put bridge paperwork there
By its own archived account, the firm is "a Disadvantaged Business Enterprise that provides qualified staff personnel to clients for roadway and bridge construction projects in the State of Florida," prequalified in FDOT Work Groups 10.1 and 10.3 and providing "CEI support services as a subconsultant to prime consultants."
That is not a procurement accident. 49 CFR Part 26 exists in part to "promote the use of DBEs in all types of federally assisted contracts", and primes meet their commitments by subcontracting. The data perimeter extends, by design, to firms selected partly because they are small. Security spend tracks revenue; the subcontracting requirement tracks the inverse.
Read the flow-down the rule mandates. § 26.13(b) requires every subcontract a prime signs to carry an assurance, and that assurance is about nondiscrimination. § 26.37(b) requires a recipient to review "contracting records" and monitor "the work site" to confirm the DBE performed the work it was committed. Neither addresses how a subconsultant stores the project records its staff produce.
The practice: enumerate accounts, not vendors
A questionnaire asks a subconsultant to describe controls on systems you do not own. What you own is the accounts you issued it, and for a staffing-shaped CEI firm that is where the exposure sits: its people work inside the prime's and the owner's systems — density log books, materials certifications, pay applications. The useful question after an intrusion there is not what sat on its file server; it is which of your systems its staff could still reach on Monday.
Run one query per system instead of one email per vendor. In Entra ID:
Connect-MgGraph -Scopes "User.Read.All","AuditLog.Read.All"
Get-MgUser -Filter "userType eq 'Guest'" -All `
  -Property DisplayName,Mail,CreatedDateTime,SignInActivity |
  Select-Object DisplayName,Mail,CreatedDateTime,
    @{n='LastSignIn';e={$_.SignInActivity.LastSignInDateTime}} |
  Sort-Object LastSignIn
Per account, answer three things: what it can export, when it last authenticated, and whose offboarding removes it. The third answer is usually "the subconsultant's HR process," which means nothing happens in your tenant when someone leaves theirs — and the scope a partner account carries is the part that surprises people.
State the costs. SignInActivity needs Entra ID P1 or P2 and AuditLog.Read.All, so this is a licence line and a privileged consent, not a free read. It will surface accounts nobody will claim. And fixing the offboarding trigger is a contract amendment: you are asking for notice of staffing changes as a deliverable. If you cannot get that this quarter, expire every external account on its task-order end date.
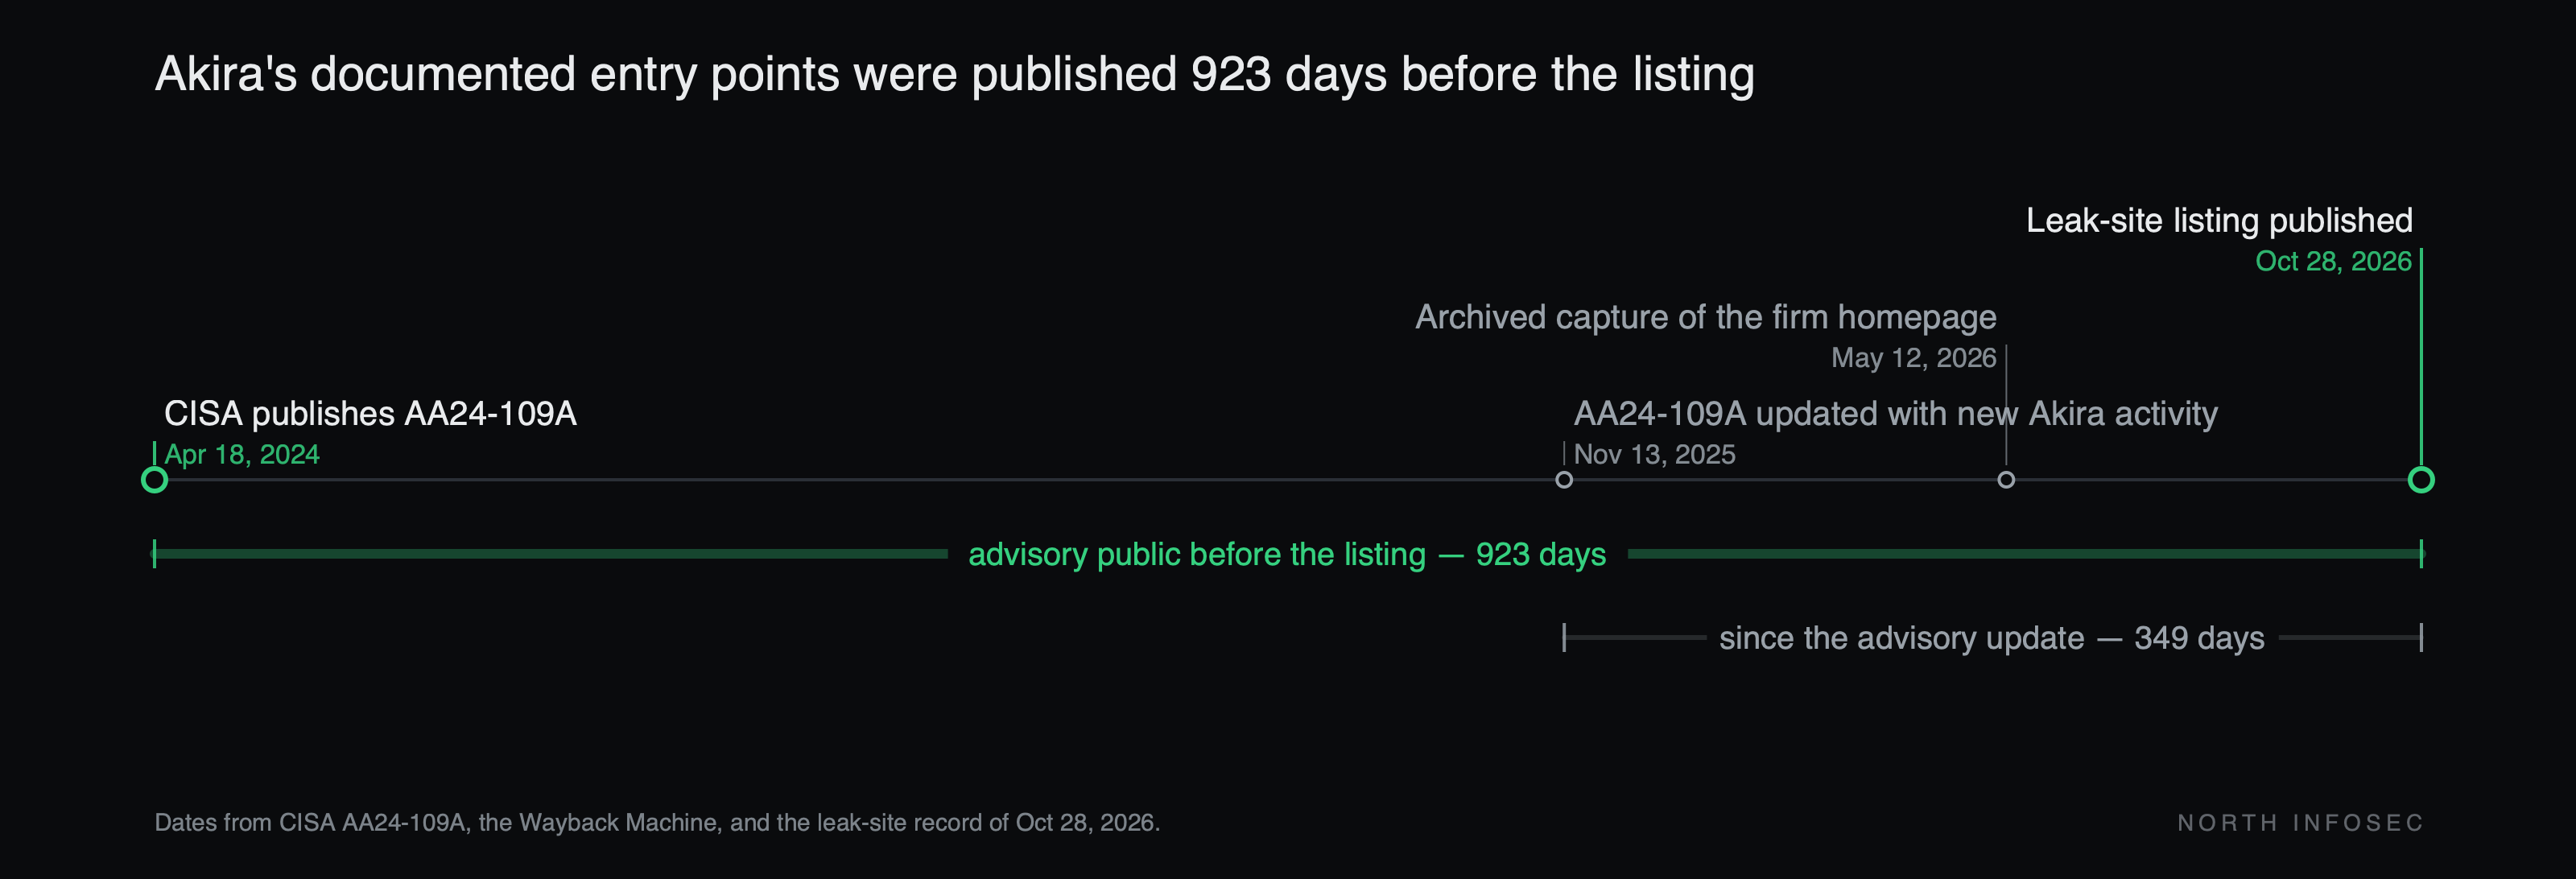
At the small end of the chain, the list is published. CISA's AA24-109A, issued April 18, 2024 and updated November 13, 2025, states that the FBI and researchers "observed Akira threat actors obtaining initial access to organizations through a virtual private network (VPN) service without multifactor authentication (MFA) configured, mostly using known Common Vulnerabilities and Exposures." It names CVE-2024-40766 (SonicWall), CVE-2023-27532 and CVE-2024-40711 (Veeam), CVE-2020-3259, CVE-2023-20269 and CVE-2020-3580 (Cisco), CVE-2023-28252, and CVE-2024-37085 (VMware ESXi). Work it in order of payoff: MFA on every remote-access path, then the backup server, the firewall firmware, the hypervisor. It is not an attribution — nothing public establishes how this firm was accessed.
How to check
- Pull the external-account list from each project document system you operate, group it by subconsultant, and compare it against the staffing roster that firm last gave you.
- Record the last authentication date per account. Anything dormant past the end of the task order it was created for is a finding, not a backlog item.
- Name, per subconsultant, who on your side learns when one of their staff leaves. If nobody can be named, the questions worth asking a breached provider arrive before the answer does.
North InfoSec runs AI-assisted penetration testing and security assessments, including third-party and supply-chain exposure of the kind described above. northinfosec.com